 Helm Sparkle
Documentation / Integrations
Okta
Connects Okta for single sign-on through SAML 2.0 and for user provisioning through SCIM.
Set up
- Open Integrations in the navigation for your role.
- Choose Add integration, then select Okta.
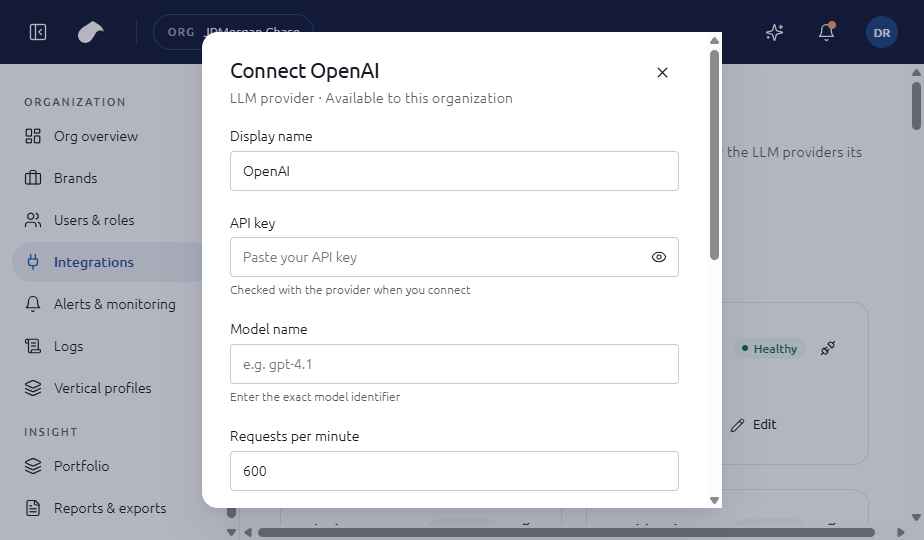
- Enter Okta domain (without https://); Client ID; SCIM token.
- Choose Connect. Helm tests the connection before it saves the integration.
If the test fails, you can choose Save without verifying. The integration is then saved with an error status until you fix it.
What the screen shows
The form asks for the Okta domain, a client ID and the SCIM token. Once connected, the integration shows SAML 2.0 with SCIM enabled. Users it provisions appear in Users and roles with the source SCIM.
Notes
- Enter the domain only, for example company.okta.com.
- Users provisioned through SCIM are managed in Okta. Change their roles there.
Last updated
Was this page helpful?Contact support